Showing posts with label PCI compliance. Show all posts

Wednesday, 11 June 2014

Paws Studio Review

By Jim Halfpenny 

About the Author 


Jim is an experienced IT practitioner with 14 years experience in both academia and industry, working with renowned companies including British Airways, Oracle, BSkyB and Cloudera.

Whether you see compliance as a burden or an aspiration we are frequently mandated to meet a certain set of security requirements around our information assets. One important aspect is being able to demonstrate to yourself and to others that your systems meet the criteria set by your compliance regime. How do you ensure that your systems are compliant with your policies or those mandated by compliance standards? A program of auditing your systems will help you understand the state of your estate.

Titania’s Paws Studio provides a means to audit Windows and Linux systems and provide compliance reports against a defined set of policies. It sets out to provide clear and detailed reports of the system’s level of compliance. Policy templates are editable and Paws Studio comes with predefined templates based on established policies and best practice including PCI, SANS and DoD STIG.

Policy templates are essentially a group of compliance audit checks built from the check library provided by Paws Studio. Checks range from high-level tests such as the presence of antimalware software right down to individual file permissions and registry settings.

There are two ways of creating and customising policy templates. The first is a wizard that guides you through creating your policy. Here you can define the rules that comprise your policy by clicking through a series of screen and selecting checks from the library. The interface is straightforward and self-explanatory and it is a great tool for less advanced users. However, the more technically minded user might find it time consuming and prefer to use the supplied Policy Editor instead which is undoubtedly the more powerful tool.

The Policy Editor provides you with a tree layout of your policy, giving you a bird’s eye view on the ability to quickly navigate through the rules.

In addition clicking on the advanced tab gives you a syntax-highlighted view of the raw policy XML. Whatever tool you choose, the result is an XML file defining the compliance checks for your policy and metadata used to generate the final compliance reports.


Once you have your policy defined it’s time to audit your systems. In order to compile a report you need the compliance audit data collected from a machine. At this point you have three options. You can choose to audit the local machine where Paws Studio is installed. You can also audit a system over the network. To do this will need valid administrator credentials on the remote system. Paws Studio will scan the local network for hosts to audit or you can specify the IP address of the machines in scope.


The third option is to use the portable data collector software, a small executable that can be run from a thumb drive. This is particularly useful where you need to audit a system that is not on the network or is air gapped from your audit workstation. Run the Data Collector, choose an audit policy and it will create a .paws file with the audit results.

Once you have collected your audit data you can produce a report on the audited system. Reports contain the result of each test on the system as well as summary charts showing percent tests passed and a breakdown of tests that failed by severity. Paws Studio creates a compliance audit report that can be saved as HTML, PDF, PostScript or Microsoft Word document. CSV and XML formats are also available so you can feed machine-readable reports into other reporting systems or build your own applications to consume your compliance data.


Paws Studio is available for Windows, Mac OS X and various flavours of Linux and currently supports auditing of Windows and Linux systems. This software pitches to the SME market who could be priced out by enterprise-grade auditing software though they are unlikely to benefit from the bells and whistles these tools provide. If you need a cost effective and easy to use compliance reporting tool, Titania’s Paws Studio certainly merits a second look.

Monday, 9 June 2014

Paws Studio Walkthrough

by Alen Damadzic (Software Developer, Titania)

About the Author

Alen is a key member of the technical team and is the lead developer of Paws Studio compliance auditing software. Since joining Titania as a computing graduate three years ago, Alen’s knowledge of software development and cyber security has grown with the company and he now uses this knowledge to support and train new members to the ever growing development team.

Paws Studio is a compliance auditing tool for servers, workstations and other Windows or Linux based systems. At a basic level, creating a compliance report in Paws Studio can be as simple as selecting an audit policy and clicking go. However, behind the scenes, Paws Studio is performing a number of different processes in order to determine what needs to be checked, collecting the data, comparing the collected data against a policy and finally creating a report. This article provides a walkthrough of those processes to enable you to create truly effective and thorough custom policies to audit against.


Figure 1. Paws Studio audit process
A typical Paws Studio audit is a two-step process. The initial step is to collect the data for the audit and the second is to create the report by comparing that data against a compliance list (see Figure 1).

Collecting Audit Data


Data, such as password policy settings, are collected using a data collector. On Windows, the data collector is a small native program that reads the registry, file permissions and so on. The data collector does not require installing on the system that is being audited and does not require anything to be installed. On Linux systems the data collector is a shell script.

The data collector only collects what is required to create the report. Those audit parameters are specified in a policy file, which we will come back to later.

Figure 2. Report creation methods

When you select to create a new report in Paws Studio (see Figure 2), it will give you the option to add all the systems that you want to audit (local and remote). Paws Studio will then deal with executing the data collector for you and retrieve the results. It is important to note that during this process, Paws Studio will tidy up after itself, so no audit files will be left on the audited system.

Figure 3. Manual data collector option
It is also possible for you to run the data collector yourself on various systems and provide Paws Studio with the collected data; this is shown as the “Manual” option (see Figure 3).

To obtain the latest data collector so that you can perform the audit yourself, select the “Export Collector” option from the “Utilities” menu. You will also need a copy of the audit policy file for the data collector. By default on a Windows system the policy files are stored in “C:\Program Files\Paws Studio\XML”. You will find policy files for PCI, STIG, SANS, and others.

The data collector can be executed from the command line on both Windows and Linux systems. This gives you the ability to script the software so you can automate the audit data collection process.

The Audit Policy


Figure 4. Audit policies

When you create a compliance audit report in Paws Studio you have to select an audit policy that you want to check compliance with. It could be a PCI policy, STIG or others. The policy that you check compliance against when producing a Paws Studio report is stored in a specially formatted XML file.

Although Paws Studio is supplied with a number of pre-defined audit policies, you can create your own. You could use your favourite XML editor to create an audit policy file but Paws Studio includes a policy editor.

The audit policy editor has two modes of operation, a wizard mode and editor mode (see Figures 5, 6). The wizard mode is designed to easily enable you to create your own new audit policy, or edit an existing one, and guide you through the process. The editor mode is more suited for advanced users and editing existing policies.

Figure 5. Policy editor: editor mode

Figure 6. Policy editor: wizard mode

Figure 7. Paws Studio Settings

Customizing an Audit Report


Your audit reports can be customized to change the company name, logo, classification and so on. If you want to override the default Cascading Style Sheet (CSS) there is even an option to do that.

Some key customization options such as the “Policy Editor” “Authorized Software” and “Authorized Startup Items” contain the lists of what is determined to be authorized or not during those particular checks.

The “Reporting” options include an “Interactive Mode” setting that will cause Paws Studio to potentially ask you some questions during an audit. For example, some checks may require a physical analysis, such as “is the server room door locked?”.

An Audit Walkthrough

Figure 8. Paws Studio main frame
Now that we have highlighted the key components of a Paws Studio audit, the simple process of performing a report with all the available options is straight forward.

Select the “Create Report” option (see Figure 8).

Figure 9. Report creation methods

Select what you want to audit (see Figure 9).

“Local” will enable you to perform an audit of your local machine.

“Network” will enable to audit other computers on the network. You many need to specify a username and password.

“Manual” will allow you to add manually collected audit data.

Figure 10. Audit policies

Select the audit policy report that you are interested in. You can select multiple audit policies or specify your own using the “Import Policy” button (see Figure 10).

Click on “Create Report”.

Then you can read your report and save it out to a number of different formats such as HTML, Word, PDF, CSV and others.

Conclusion


This article has delved into what goes on behind the scenes of Paws Studio. By walking you through the key processes involved in creating your own compliance reports, it will enable you to get the most out of the software.

Thursday, 8 May 2014

Plaudits for the PCI Audits


First published in Computing Security magazine


By Ian Whiting (CEO, Titania) 

About the Author 

Ian has been working with leading global organizations and government agencies to help improve computer security for more than a decade. He has previously been accredited by CESG for his security and team leading expertise for over 5 years. In 2009 Ian Whiting founded Titania with the aim of producing security auditing software products that can be used by non-security specialists and provide the detailed analysis that traditionally only an experienced penetration tester could achieve.

Non-compliance is no longer an option, yet conflicting views still exist upon compliance and security, and what they mean for an organisation. After numerous high-profile breaches (Target, Neiman Marcus), PCI DSS has come heavily under the spotlight. The full extent of these attacks is yet to be revealed, but the compliance industry is already changing to cater to the ever-increasing threats and vulnerabilities that affect the card payment protection industry.

PCI DSS 3.0, which was announced in November 2013, will remain under 'best practice' guidelines until 30 December 2014. The new version addresses some of the issues reported by the industry, such as education, awareness, securing cardholder data and inconsistency in assessments, which have led to poor security practices and compliance failures.

CHANGES TO PENETRATION TEST REQUIREMENTS 
According to Verizon's 2014 PCI Compliance Report, Requirement 11 'was the least complied-with requirement […]. Just 23.8% of companies met all the controls between 2011 and 2013'. Requirement 11 concerns vulnerability scanning and penetration testing, and 11.3 in particular specifically deals with the demands of penetration testing. Outlined below are three major changes to Requirement 11:

1. External and internal penetration testing is to be carried out at least annually. This also requires tests to be performed after significant infrastructure or application upgrades. Recommendations include the tests to be performed by a qualified internal resource or a qualified external third-party, according to a defined methodology. In this case, the tester is not required to be a QSA or ASV (Approved Scanning Vendor).

2. Fix exploitable vulnerabilities found during penetration testing and repeat testing to verify corrections. The tests should be undertaken at least annually and after significant changes to the environment - eg, an operating system upgrade or web server additions.

3. Annual penetration tests that verify segmentation is used to isolate the Cardholder Data Environment (CDE). PCI DSS 3.0 guidance advises that penetration testing is to be used to assess how effective the segmentation that isolates CDE from other networks is. It specifies that the testing methodology should be reviewed to ensure all segmentation methods are covered, as well as verifying there is no connectivity between in-scope and out-of-scope networks. The tests should be performed annually and in light of any changes to segmentation controls or methods. These changes outline that, in order to combat the increasing threat, the detail and frequency of internal and external audits needs to increase (especially after system upgrades).

Although some worry that this will put extra time and financial pressures on companies meeting the PCI DSS standard, the reality is that the quality and frequency of tests is often sacrificed by companies for the sake of 'ticking the box'. The refined recommendations for defined methodologies and specified frequency should, in fact, help level the market and provide a fair deal to organisations shopping around for the best pen testing solutions.

Although some PCI requirements are such that no tool can truly perform a fully automated assessment, there is a plethora of cost-effective auditing tools that can help increase speed and accuracy of PCI audits. These can not only be used to ease the cost of internal audits, but also by pen testers to offer more thorough assessments without significantly impacting costs.

Thursday, 3 April 2014

Interop 2014 - What's Hot in Network Security? PCI DSS 3.0, Compliance & National Defence

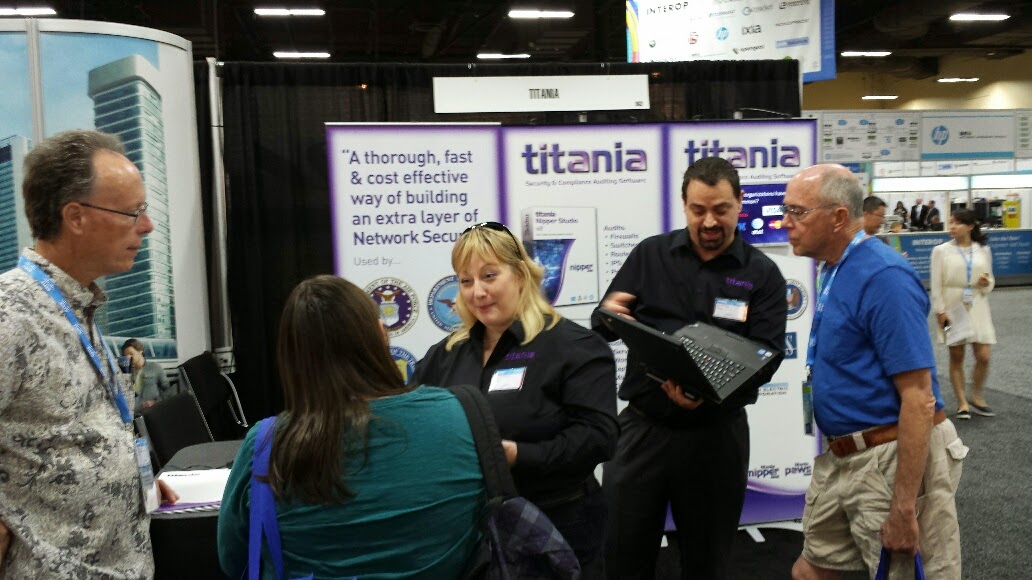
The last day of the Interop Exhibition has come, so here is an overview of what's been happening so far, in the words of the Titania team greeting you at our stand in Las Vegas: Ian Whiting, Nicola Whiting & Andy Williams. 


Ian Whiting & Andy Williams - setup and ready for Interop
Andy Williams, Head of International Development: "On the first day of Interop we met with a wide variety of IT professionals from business, government and academia, not only from the US but around the world - including Australia, Europe, Asia and the Middle East. Visitors are interested to learn that, although we are a small business based in the UK, we are truly international with clients in 60 countries worldwide."


Andy Williams explaining why Titania is expanding so fast globally
Nicola Whiting is Titania's Chief Operations Officer and she was pleased to notice that "information security is a hot issue at the show with several of the leading network security device vendors present - including those whose devices we support such as Cisco, Dell, HP, Watchguard, Barracuda, and F5."


Nicola Whiting is happy to see that information security is a priority for Interop 2014


Finally, Ian Whiting (CEO) has been in Las Vegas for all three days to answer questions and discuss the latest developments of Nipper Studio 2.3: "Titania’s booth is adjacent to that of the US Government’s National Security Agency. Visitors have been impressed by the fact that Titania supplies extensively to the US government’s security and defence community, as well as to many federal civil agencies.

The person who has all the answers on Nipper Studio -  its developer, Ian Whiting...

... And he loves to demo

IT security representatives from a number of major international corporations such as Bridgestone and Visa have stopped by to catch up on what’s new in the latest versions of our security and compliance audit software. Many have commented favourably on the latest features in the latest release of Nipper Studio. PCI DSS 3.0 compliance reporting functionality in both Nipper Studio and Paws Studio is proving of particular interest."

Update: Day 2 at Interop continued to be very busy and productive for Titania with some of the world's leading technology companies including VMware, Fujitsu and Microsoft taking time to visit us at our booth. It was also great to meet with new contacts from among our US government client base, including the US Navy, The show has also been useful in connecting with a number of leading system integrators, resellers and managed service providers interested in exploring partnerships with Titania as we rapidly expand our US market presence. 

It is great to see such positive feedback, from our customers and visitors alike. Thank you for making Interop 2014 a memorable experience. 

And we look forward to seeing more familiar faces at next year's Interop.

Friday, 21 February 2014

Nipper Studio 2.3 Now Released


NipperStudio 2.3 is now available and contains both new features and advancements to the underlying audit technology, providing updates that will benefit all users.


Existing Users: Next time you run Nipper Studio and perform a software update check you will be prompted to download the new version. The latest version can also be manually downloaded by logging on to your Titania account.


New Users: Log on to your Titania account and download the latest version from the Titania web site.


New and Improved Features in Nipper Studio 2.3

·         PCI DSS 3 reporting, using the latest version of the PCI DSS compliance standards. To help make the PCI DSS process simpler, interactive options are available to step the auditor through the process of checking any non-automated elements (e.g. is the documentation up to date?)

·         Vastly improved software vulnerability analysis with the inclusion of the NIST (National Institute of Standards and Technology) NVD (National Vulnerability Database). Plus integration of the vulnerability analysis with OVAL (Open Vulnerability and Assessment Language) templates.

·         STIG improvements with better reporting of findings, the collating of results, better interactive options and more automation of some findings.

·         Improved selection of date formatting including the addition of ISO 8601 date formats.

·         Improved HTML reporting with support for themes using CSS (Cascading Style Sheets). The old reporting theme is also included as the “Classic” theme.

·         Vastly enhanced remote connectivity capabilities using XML-based definitions, enabling the easy expansion of the capability by both users and Titania. Additionally, remote connectivity is now also available from the command line.

·         A new resource manager to enable the ease of updating the resources such as NVD, STIG and OVAL templates. So if a new STIG is released, or an internal version is maintained, then it can easily be imported in to Nipper Studio for immediate use.

·         Improvements with extended characters within device configurations and reports with the full adoption of Unicode throughout.


If you have any questions or would like more information about any of the new  or existing features in Nipper Studio then please don’t hesitate to get in touch.


Thursday, 30 January 2014

Target. A Series of Unfortunate Events


Source: yahoo.news.com


It started right before the holidays, with Brian Krebs’ first report on a 40 mil. financial data breach at Target stores.  News followed that a further 70 mil. accounts containing personal identifiable information was also compromised during the heist.

From then on the focus was on how  the breach happened, what software was deployed, where did Target go wrong and who should take the best part of the blame. Meanwhile, Target provided customers with a sign up for free credit monitoring and identity theft protection system and announced it will invest $5mil in a brand new cyber security coalition. 

But that’s not the end of the problems for the retailer.

Alongside Target, the retail industry is experiencing a surge in cyber attacks and POS malware. The FBI re-assures us that they are aware of these attacks and they are not likely to stop. Compliance is widely criticised as Target was in fact compliant with the PCI DSS standards and it did nothing to stop these spectacular attacks. 

However the infosec community is looking at the entire story with a shaking head and a look of “I told you so”, because researchers have long stated that compliance does not mean security. Previous incidents at Wall-Mart and Heartland Payment Systems had left an even more embarrassing mark on compliance, as they were certified compliant while their networks were in the process of being hacked.

The implications of these recent hacks are wide and diverse. Banks will tighten their liability policies, payment providers will continue to issue fines for poor cyber security measures, while retailers deal with bad publicity and falling share prices. 
This in turn affects economies and market statutes while the customer is left in the middle with the choice of a week’s worth of hassle for cancelling a compromised card and/or the expense of a lawsuit against the retailer.

It seems that all these industries should take a break from trying to only protect themselves and come together for a long-term cooperation strategy centered around the key player: the consumer.  As it stands every industry is furiously trying to escape the responsibility and pass an already irritated and distrustful victim from one institution to another. 

This may work for the time being, but will only lead to a deeper lack of trust in a flawed system.  There is more to be done to educate, prevent and restore trust, and this will take a cooperative and supportive effort from all the industries if they continue to expect customers to hand over their data. 


Tuesday, 10 December 2013

What Is PCI Compliance?


PCI Compliance – Payment Card Industry Data Security Standard is a set of requirements designed to ensure all businesses which handle credit card information maintain a secure environment. It was created by the five major card schemes like American Express, JCB, Visa, MasterCard and Discover Financial Services to prevent and reduce card data fraud. Even though it does not have any legislative power the regulators can apply fines, or increase transaction fees or terminate the relationship with the merchant.

Source: bigcommerce.com
PCI compliance came about in order to improve payment procedure security, but the responsibility to enforce compliance lies with the merchants and customers not with the PCI council.

Even more to the benefit of individuals running businesses from home, PCI compliance can at least offer guidance on security measures, since intruders do focus on the home users as “easy targets” with home run applications that are not adequately protected.

For all external facing IP address merchants that store cardholder data, a quarterly scan by a PCI Approved Scanning Vendor is compulsory to validate the compliance.

Usually for a merchant to be declared compliant, the process will involve internal scans, penetration tests and file monitoring for the cardholder data environment. If customers need transference to a third-party website during transaction, then the third-party IP address needs to be submitted to the scan as well.

PCI DSS guide on security requirements consists of six rules:
·         Build and maintain a secure network and systems
·         Protect cardholder data
·         Maintain a vulnerability management program
·         Implement strong access control measures
·         Regularly monitor and test networks
·         Maintain an information security policy


PCI compliance council categorises merchants under 4 levels:
1.       Merchants processing over six million Visa transactions per year, regardless of transaction channel.
2.       Merchants processing one million to six million Visa transactions per year, regardless of transaction channel.
3.       Merchants processing 20,000 to 1 million Visa transactions per year, e-commerce transactions.
4.       Merchants processing fewer than 20,000 Visa e-commerce transaction, and all other merchants processing up to 1 million Visa transactions per year, regardless of transaction channel.