Showing posts with label PCI DSS 3. Show all posts

Thursday, 8 May 2014

Plaudits for the PCI Audits


First published in Computing Security magazine


By Ian Whiting (CEO, Titania) 

About the Author 

Ian has been working with leading global organizations and government agencies to help improve computer security for more than a decade. He has previously been accredited by CESG for his security and team leading expertise for over 5 years. In 2009 Ian Whiting founded Titania with the aim of producing security auditing software products that can be used by non-security specialists and provide the detailed analysis that traditionally only an experienced penetration tester could achieve.

Non-compliance is no longer an option, yet conflicting views still exist upon compliance and security, and what they mean for an organisation. After numerous high-profile breaches (Target, Neiman Marcus), PCI DSS has come heavily under the spotlight. The full extent of these attacks is yet to be revealed, but the compliance industry is already changing to cater to the ever-increasing threats and vulnerabilities that affect the card payment protection industry.

PCI DSS 3.0, which was announced in November 2013, will remain under 'best practice' guidelines until 30 December 2014. The new version addresses some of the issues reported by the industry, such as education, awareness, securing cardholder data and inconsistency in assessments, which have led to poor security practices and compliance failures.

CHANGES TO PENETRATION TEST REQUIREMENTS 
According to Verizon's 2014 PCI Compliance Report, Requirement 11 'was the least complied-with requirement […]. Just 23.8% of companies met all the controls between 2011 and 2013'. Requirement 11 concerns vulnerability scanning and penetration testing, and 11.3 in particular specifically deals with the demands of penetration testing. Outlined below are three major changes to Requirement 11:

1. External and internal penetration testing is to be carried out at least annually. This also requires tests to be performed after significant infrastructure or application upgrades. Recommendations include the tests to be performed by a qualified internal resource or a qualified external third-party, according to a defined methodology. In this case, the tester is not required to be a QSA or ASV (Approved Scanning Vendor).

2. Fix exploitable vulnerabilities found during penetration testing and repeat testing to verify corrections. The tests should be undertaken at least annually and after significant changes to the environment - eg, an operating system upgrade or web server additions.

3. Annual penetration tests that verify segmentation is used to isolate the Cardholder Data Environment (CDE). PCI DSS 3.0 guidance advises that penetration testing is to be used to assess how effective the segmentation that isolates CDE from other networks is. It specifies that the testing methodology should be reviewed to ensure all segmentation methods are covered, as well as verifying there is no connectivity between in-scope and out-of-scope networks. The tests should be performed annually and in light of any changes to segmentation controls or methods. These changes outline that, in order to combat the increasing threat, the detail and frequency of internal and external audits needs to increase (especially after system upgrades).

Although some worry that this will put extra time and financial pressures on companies meeting the PCI DSS standard, the reality is that the quality and frequency of tests is often sacrificed by companies for the sake of 'ticking the box'. The refined recommendations for defined methodologies and specified frequency should, in fact, help level the market and provide a fair deal to organisations shopping around for the best pen testing solutions.

Although some PCI requirements are such that no tool can truly perform a fully automated assessment, there is a plethora of cost-effective auditing tools that can help increase speed and accuracy of PCI audits. These can not only be used to ease the cost of internal audits, but also by pen testers to offer more thorough assessments without significantly impacting costs.

Thursday, 3 April 2014

Interop 2014 - What's Hot in Network Security? PCI DSS 3.0, Compliance & National Defence

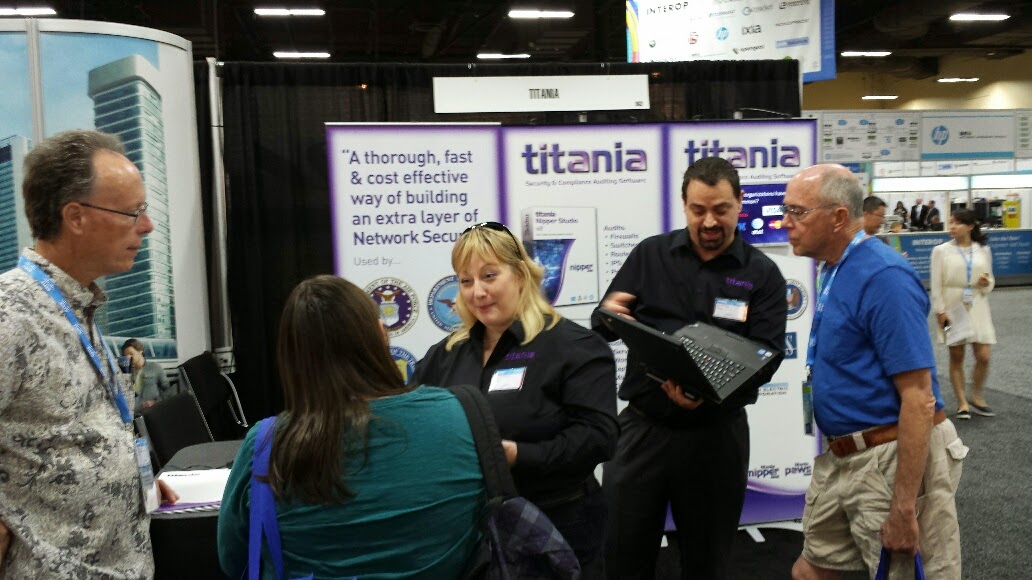
The last day of the Interop Exhibition has come, so here is an overview of what's been happening so far, in the words of the Titania team greeting you at our stand in Las Vegas: Ian Whiting, Nicola Whiting & Andy Williams. 


Ian Whiting & Andy Williams - setup and ready for Interop
Andy Williams, Head of International Development: "On the first day of Interop we met with a wide variety of IT professionals from business, government and academia, not only from the US but around the world - including Australia, Europe, Asia and the Middle East. Visitors are interested to learn that, although we are a small business based in the UK, we are truly international with clients in 60 countries worldwide."


Andy Williams explaining why Titania is expanding so fast globally
Nicola Whiting is Titania's Chief Operations Officer and she was pleased to notice that "information security is a hot issue at the show with several of the leading network security device vendors present - including those whose devices we support such as Cisco, Dell, HP, Watchguard, Barracuda, and F5."


Nicola Whiting is happy to see that information security is a priority for Interop 2014


Finally, Ian Whiting (CEO) has been in Las Vegas for all three days to answer questions and discuss the latest developments of Nipper Studio 2.3: "Titania’s booth is adjacent to that of the US Government’s National Security Agency. Visitors have been impressed by the fact that Titania supplies extensively to the US government’s security and defence community, as well as to many federal civil agencies.

The person who has all the answers on Nipper Studio -  its developer, Ian Whiting...

... And he loves to demo

IT security representatives from a number of major international corporations such as Bridgestone and Visa have stopped by to catch up on what’s new in the latest versions of our security and compliance audit software. Many have commented favourably on the latest features in the latest release of Nipper Studio. PCI DSS 3.0 compliance reporting functionality in both Nipper Studio and Paws Studio is proving of particular interest."

Update: Day 2 at Interop continued to be very busy and productive for Titania with some of the world's leading technology companies including VMware, Fujitsu and Microsoft taking time to visit us at our booth. It was also great to meet with new contacts from among our US government client base, including the US Navy, The show has also been useful in connecting with a number of leading system integrators, resellers and managed service providers interested in exploring partnerships with Titania as we rapidly expand our US market presence. 

It is great to see such positive feedback, from our customers and visitors alike. Thank you for making Interop 2014 a memorable experience. 

And we look forward to seeing more familiar faces at next year's Interop.

Friday, 21 February 2014

Nipper Studio 2.3 Now Released


NipperStudio 2.3 is now available and contains both new features and advancements to the underlying audit technology, providing updates that will benefit all users.


Existing Users: Next time you run Nipper Studio and perform a software update check you will be prompted to download the new version. The latest version can also be manually downloaded by logging on to your Titania account.


New Users: Log on to your Titania account and download the latest version from the Titania web site.


New and Improved Features in Nipper Studio 2.3

·         PCI DSS 3 reporting, using the latest version of the PCI DSS compliance standards. To help make the PCI DSS process simpler, interactive options are available to step the auditor through the process of checking any non-automated elements (e.g. is the documentation up to date?)

·         Vastly improved software vulnerability analysis with the inclusion of the NIST (National Institute of Standards and Technology) NVD (National Vulnerability Database). Plus integration of the vulnerability analysis with OVAL (Open Vulnerability and Assessment Language) templates.

·         STIG improvements with better reporting of findings, the collating of results, better interactive options and more automation of some findings.

·         Improved selection of date formatting including the addition of ISO 8601 date formats.

·         Improved HTML reporting with support for themes using CSS (Cascading Style Sheets). The old reporting theme is also included as the “Classic” theme.

·         Vastly enhanced remote connectivity capabilities using XML-based definitions, enabling the easy expansion of the capability by both users and Titania. Additionally, remote connectivity is now also available from the command line.

·         A new resource manager to enable the ease of updating the resources such as NVD, STIG and OVAL templates. So if a new STIG is released, or an internal version is maintained, then it can easily be imported in to Nipper Studio for immediate use.

·         Improvements with extended characters within device configurations and reports with the full adoption of Unicode throughout.


If you have any questions or would like more information about any of the new  or existing features in Nipper Studio then please don’t hesitate to get in touch.